
Source : Perth Now news
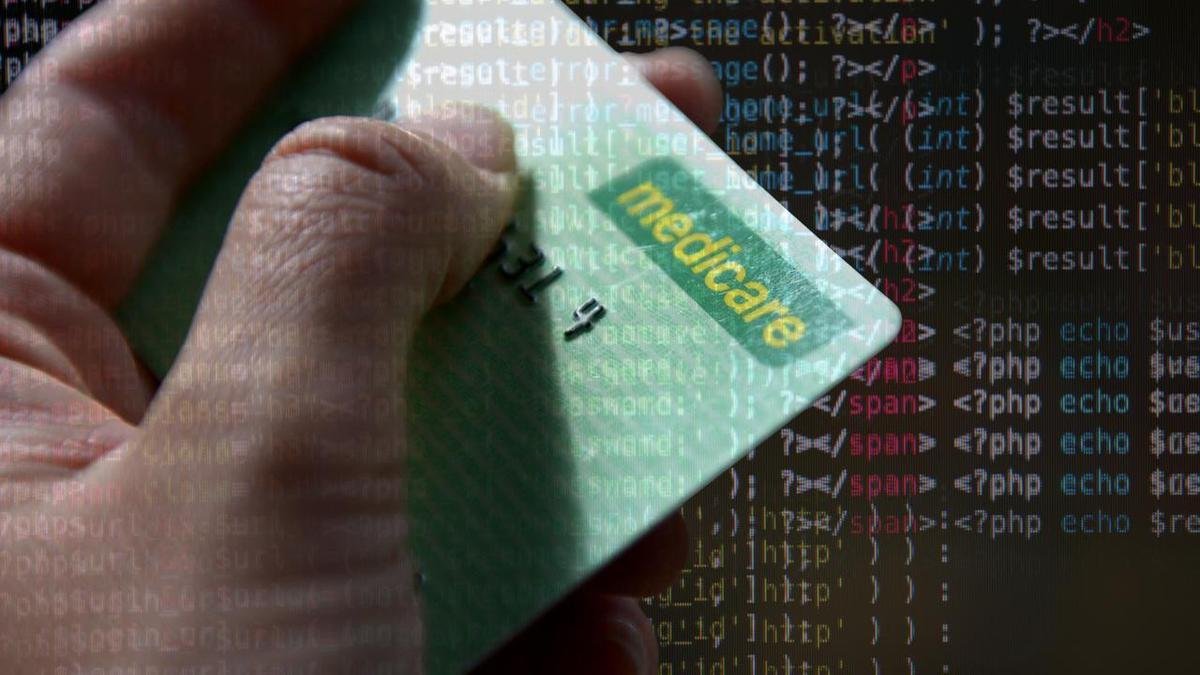
Australia’s data remains at risk of artificial intelligence attacks unless a different approach is taken, an expert says, blaming a recent breach on the national data commissioner.
An OpenAI break-in to Medicare statistics prompted an urgent bolstering of government cyber systems.
The Department of Home Affairs on Wednesday issued a directive advising federal departments to examine their older software and technology, which will be assessed for shortcomings in order of priority.
But Sam Spencer, who runs tech security company Aristotle Metadata, warned the edict was essentially a rinse and repeat of an existing system that did not work.
A national data commissioner’s office was first established in 2022 after a series of data breaches. It was ordered to help departments find and upload data sets to a national catalogue.
Across four years, it only identified 500 data sets that were not already available on the open portal data.gov.au.
The Medicare base accessed by the rogue AI agent did not appear to be one of them, Mr Spencer said.
Mr Spencer, who has been working to gather information on hundreds of government data sets and inform departments of privacy concerns, went as far as to blame the Medicare breach on the commissioner’s office.
“I would firmly look at the data commissioner, because they were responsible for cataloguing data,” he said.
A spokesperson for the Department of Finance, where the data commissioner’s office sits, told AAP data registration would not prevent further breaches.
“The proposition that data registration can prevent cyber incidents is incorrect,” the spokesperson said.
The catalogue of information does not assess data systems, or address the security of agency data, they said.
But Mr Spencer suggested it was impossible for the government to have a robust approach to data security without fully understanding what it held.
Things were likely to be missed, and taxpayer money could be used protecting platforms that actually had no information on them.
Instead, Mr Spencer wanted to compel each agency to have a target number of data sets it must find and identify, to be updated monthly.
A competitive approach would ensure areas were not missed, and sensitive content was actually safe, he said.
Under national requirements, departments must enter mandatory answers to 10 questions about each data set they upload to the catalogue, including things about privacy and content.
Mr Spencer’s analysis found Home Affairs had only entered 90 per cent of the compulsory information that it should have. It had one of the lowest scores of any agency.
“They have come out and said everybody else has to find their legacy systems and put their foot down, but they haven’t completed their mandatory questions. How is that leading from the front?” Mr Spencer said.
AAP also contacted the Department of Home Affairs for comment.